All Categories
Featured
How GCC Startups Thrive in the AI Market
Table of Contents
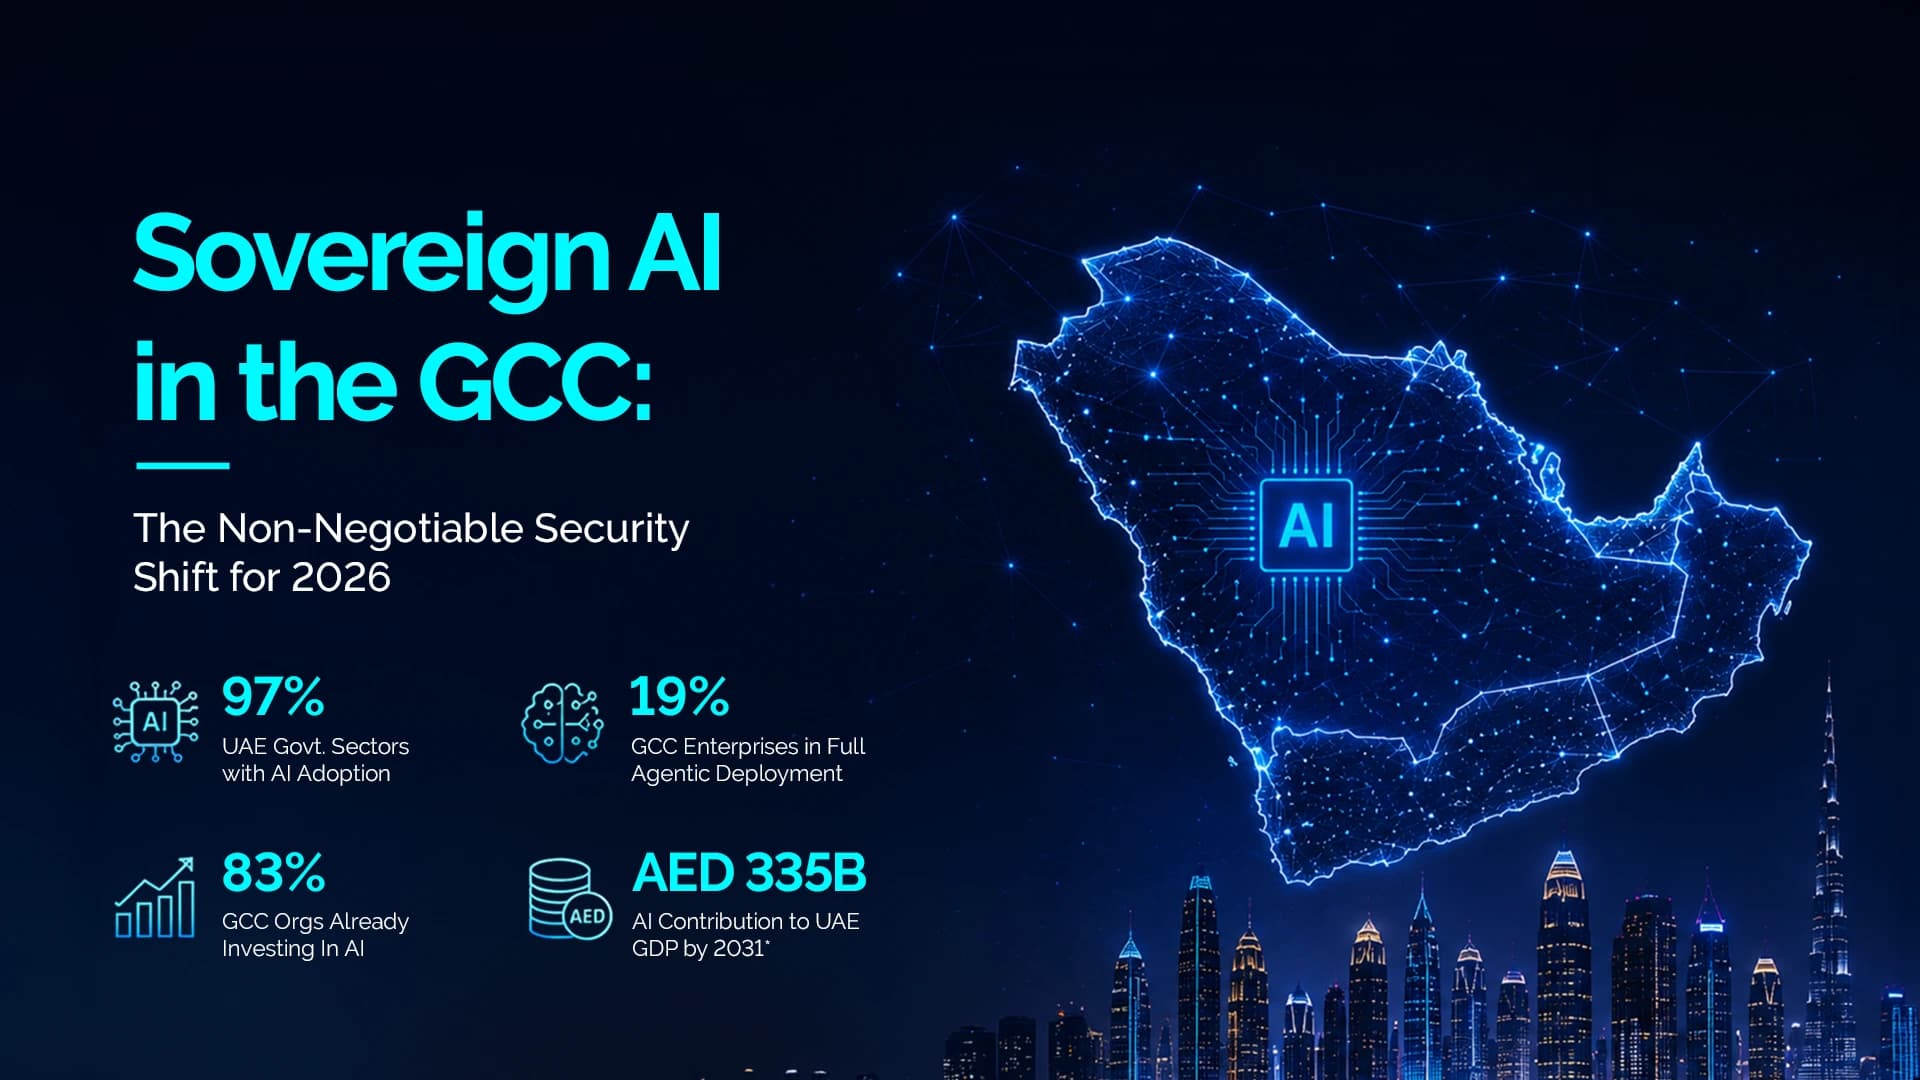
Information gotten and analyzed by "Arabi Post" on the map of cloud service centers and regions (data centers) in the Middle East and North Africa exposed that the region's countries rely heavily on American business for cloud services. The information shows the existence of around 31 American centers, the majority of them in Gulf countries, while the number of centers owned by Chinese companies reached about 7.
In the Gulf countries, more than 53% of the cloud facilities tracked there is American. Iran, meanwhile, appears to be an extraordinary case amongst all the area's countries, as it relies totally on a 100% local cloud community. 89cloud centers throughout 22 countries 35%American business' share (31 centers) 53%Gulf dependence on U.S.
Click any point to see information about the center, consisting of the running business, its nationality, and the year it was launched. Use the filters to focus on a specific nationality, or search for a specific center or country. Source: "Arabi Post" database of cloud service centers in the Middle East and North Africa (89 centers).
Within a few years, cloud service centers have actually moved from a "technical alternative" for decreasing server costs into crucial facilities for the state and the economy: e-government portals, payment and banking systems, health and education platforms, and the operation of huge information, expert system, and more. However the recent Iran war (2026) exposed a brand-new dimension: the cloud itself can be directly and physically targeted, as occurred when Iranian drone strikes damaged Amazon AWS cloud service data centers in the UAE and Bahrain, triggering interruptions and service failures.
Role of AI in 2026 Market Growth
But the significance of American and foreign business does not stop at technical competitors or service quality; it encompasses digital sovereignty and concerns of control over data for these nations and their numerous delicate sectors. American companies are subject to U.S. laws regulating legal access to data, such as the CLOUD Act, raising concerns about the limits of judicial demands for data even when it is kept outside the United States.
"CLOUD Act" (March 2018): Section 2713 clearly compels communications and computing service suppliers to protect and reveal subscriber information within their "ownership, custody, or control, regardless of whether it lies within or outside the United States" verifying the point above. (Click an image to see it full size.) This dependence also intersects with the context of cross-border intelligence gathering under frameworks such as FISA Area 702, as presented by U.S
At the very same time, experts gotten in touch with by "Arabi Post" warn of the dangers of concentrating contracts with American cloud company, and of the impact of "foreign jurisdiction" on personal privacy and security. In between issues over sovereignty and the market's need for ready-made facilities, the value of information localization policies and the limitations of cross-border information streams is growing, as gone over in worldwide reports such as those by the OECD.
Evaluating Cloud Systems for Middle East
citizens or residents who connect with individuals or organizations in those countries where data centers operated by American business keep the information of those nations and their citizens. To understand the scope of this danger, it is necessary to first analyze U.S. federal laws such as FISA Section 702 and the CLOUD Act, which governs U.S.
Although the CLOUD Act grants Washington broad authority to gain access to data saved in data centersthe massive facilities utilized by business to shop and procedure informationin some cases, under the Act, U.S. authorities might be needed to inform the government of the nation concerned that there is a legal basis engaging access to that information.
The U.S. federal government might likewise penalize or target any U.S. resident who participates in monetary transactions with that nation or sends money transfers to people there. Abu Al-Saad likewise states that if a dispute were to occur between that country and Washington, the United States might suspend its data storage services for that country and validate doing so.
This would impact all sectors, consisting of monetary and banking services. In the context of the security risks connected to nations' dependence on American information centers, another point also emergesone that Ibtihal Abu Al-Saad considers the most essential and most harmful: the U.S. legal and intelligence tool called "National Security Letters" (NSLs).
How to Leverage AI for Maximum Tech ResultsHow to Build Roadmaps for AI in 2026
federal intelligence and security firms. Under these letters, U.S. authorities have the ability to force significant innovation companies to turn over sensitive information related to citizens or countries. Washington could, for example, force Amazon to open information records coming from users in Saudi Arabia, Qatar, Bahrain, or elsewhere, while "imposing a stringent nondisclosure order that prevents the innovation business from alerting the Bahraini federal government or the targeted people that this gain access to has actually occurred.

Latest Posts
Recent GCC Tech Innovation Trends
The Best Workflow Tools Analyses in 2026
New Venture Updates From the GCC Startup Sector